Cyberespionage group linked to China focuses operations on Latin America
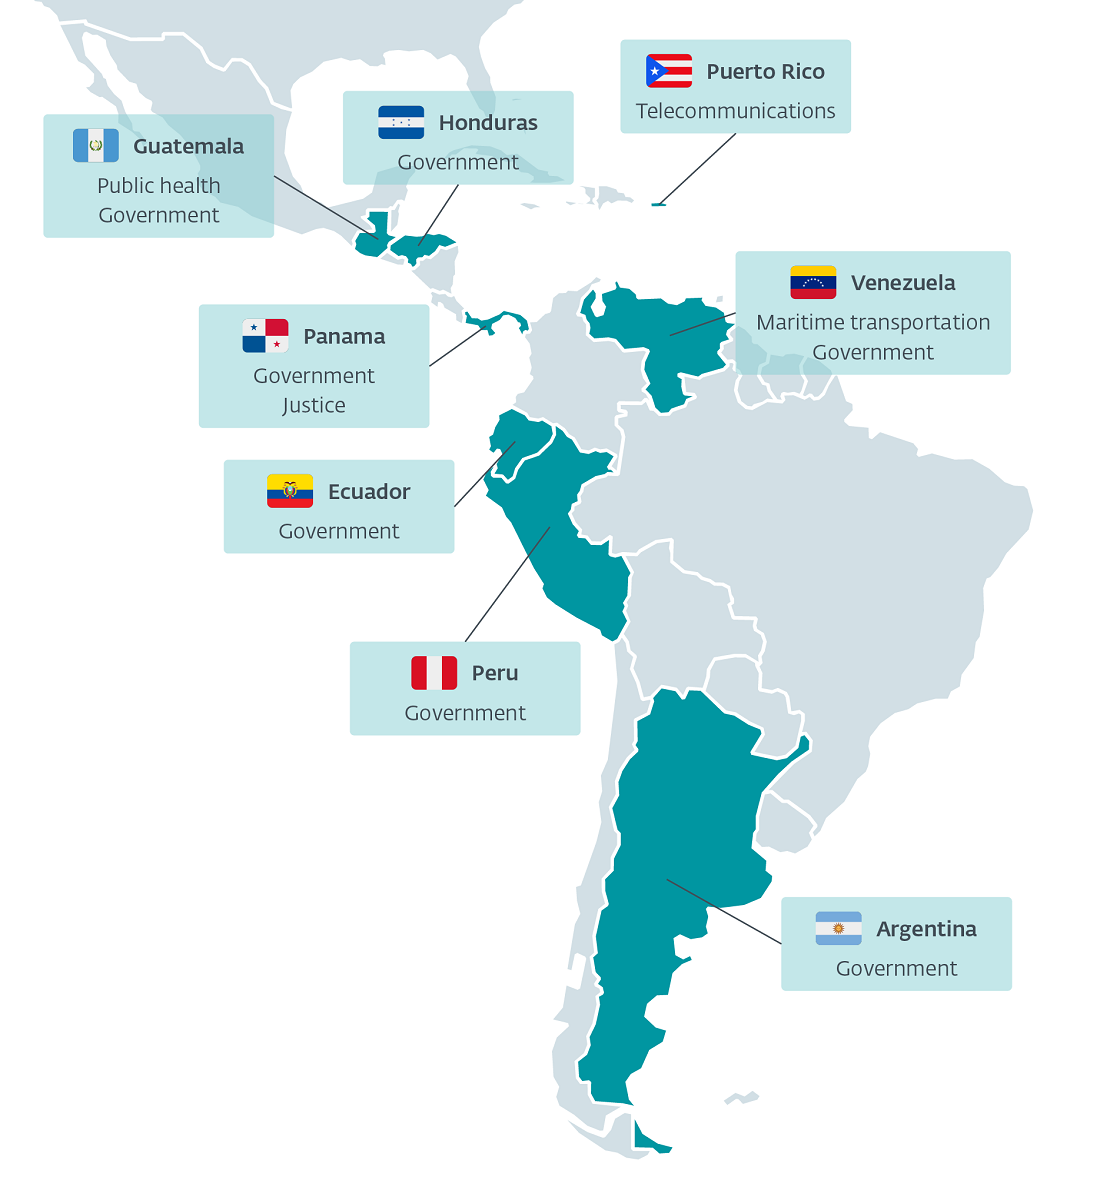
The group was identified targeting government entities in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela
New movements by the cybercriminal group “FamousSparrow,” an APT (prolonged and stealthy cyberattack) where an intruder gains access to a network and remains hidden for a period of time to steal data or spy, have been revealed, reported ESET, a leading company in proactive threat detection. This time, ESET discovered that the group has deployed a new backdoor — hidden code in a program or system that allows unauthorized access and bypasses security — targeting several Latin American countries, at least since August 2025.
“We believe this geographic focus is not accidental and likely reflects China’s response to various recent US initiatives in the region. In fact, Donald Trump’s second presidential term has seen an aggressive reassertion of US interests in Latin America, which puts several strategic investments that China has developed on the continent over the last decade in sectors such as energy, mining, and telecommunications at risk. We suspect that FamousSparrow’s activities aim to help China better monitor and anticipate the reactions of local governments to current US pressure,” commented the ESET research team.
FamousSparrow is a Chinese-linked cyberespionage group believed to have been active since at least 2019. Initially known for targeting hotels worldwide, it has also targeted governments, international organizations, trade associations, engineering firms, and law firms.
Currently, the group appears to be focusing on high-profile targets in Latin America. This trend reportedly began in July 2025 and has continued with the arrival of a new backdoor dubbed SparroWocky by ESET. In fact, between mid-2025 and 2026, 90% of the group’s targets recorded in ESET telemetry were located in the region.
Prolonged and stealthy cyberattack
ESET observed the deployment of the new backdoor against government entities in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela. This is an unusual case among the Chinese-linked APT groups that the research team had been monitoring, as their operations were typically spread across different regions of the world over extended periods.
While ESET states that it is still unclear whether the group’s apparent focus on Latin America is due to a formal geographic mandate or a temporary priority driven by current geopolitical circumstances, some cases seem to support the latter hypothesis. For example, one of the Panamanian entities identified by ESET as a target is directly involved in the trade dispute surrounding two major ports in the canal area, which until recently were operated by a Chinese-based company.
Given that the concession granted to that company was legally questioned by the Panamanian government at the beginning of 2025, ESET comments that it could be likely that the FamousSparrowgroup operation sought to obtain advance and privileged information about the intentions of local authorities regarding this matter.
Regarding the novelty of this discovery by ESET is the identification of SparroWocky, a new custom backdoor developed in C++, which incorporates more sophisticated evasion techniques to go unnoticed. This backdoor with extensive capabilities manipulates low-level structures in memory and modifies code at runtime to evade detection.
Additionally, it has the ability to load and run Beacon Object Files (BOF), a special type of executable file supported by numerous network teaming and penetration testing tools. The backdoor allows FamousSparrow to have the development capabilities necessary to integrate code from open source projects directly into its own custom backdoor.
ESET invites you to learn more about computer security and this finding by visiting: https://www.welivesecurity.com/es/investigaciones/famoussparrow-america-latina-sparrowocky/.
To obtain other useful preventive data, it is also available in Venezuela: https://www.eset.com/ve/, and its social networks @eset_ve. Also Instagram (@esetla) and Facebook (ESET).
With information and reference images provided by ESET and Comstat Rowland
Follow our news on Google! For current, interesting, and accurate information, click here to see all the content on Bitfinance.news. You can also find us on X/Twitter and Instagram